Crypto Regulation Is Moving From Token Classification to Activity-Based Licensing
Press Release | Sat Sep 12 2026
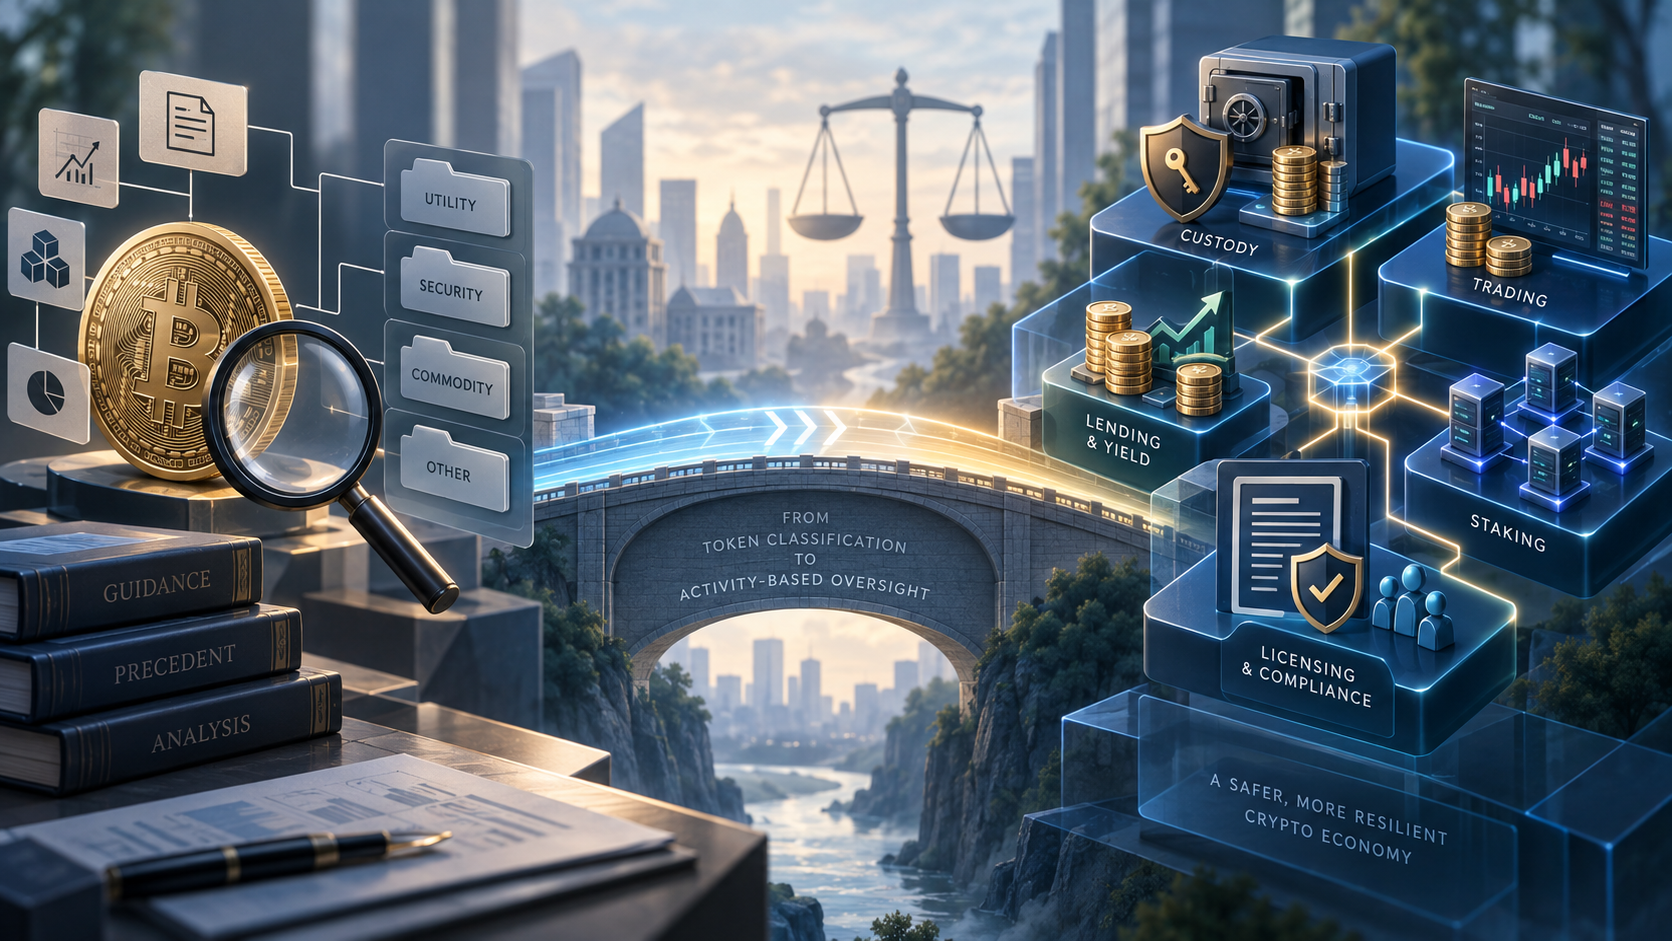
Crypto regulation spent years asking one question louder than almost every other: is this token a security?
That question still matters. It determines how an asset can be issued, marketed and distributed in many jurisdictions. But it is increasingly insufficient for an industry where the same cryptoasset can be traded, custodied, lent, staked, transferred or used as collateral through several different intermediaries.
A second question is becoming just as important: what is the firm actually doing?
That shift is visible in regulatory frameworks that impose obligations according to the service being provided rather than relying only on the legal classification of the underlying token.
The European Union's Markets in Crypto-Assets Regulation, or MiCA, is one of the clearest examples. It defines a range of crypto-asset services separately, including custody, operating a trading platform, exchanging cryptoassets, executing and transmitting orders, providing advice, portfolio management and transfer services.
The distinction has practical consequences. Under MiCA, the authorization and obligations of a crypto-asset service provider depend in part on the activities it performs. Custody comes with requirements around client agreements and records of customer positions. Trading platforms face rules on admission, market operation and orderly trading. Firms executing orders must follow execution requirements.
ESMA has also made the underlying principle explicit in its guidance: supervisors should look at the operational reality of a provider's activity rather than relying only on the terminology the company uses in contracts or marketing.
That is a significant regulatory idea for crypto.
Calling something a wallet does not answer whether a company is controlling customer assets. Calling a service a swap interface does not determine whether the provider is operating a trading venue, acting as principal or routing orders. The label matters less when regulators can examine what actually happens to the customer's asset and order.
The United Kingdom is moving in a similar direction, although through a different legal structure.
The UK's new cryptoasset regime, whose broader authorization requirements are scheduled to apply from October 2027, identifies specific regulated activities including safeguarding cryptoassets, operating trading platforms, dealing, arranging transactions and staking. FCA rules also address cryptoasset lending and borrowing as distinct activities with their own conduct and consumer-protection requirements.
That does not mean Europe and the UK have created identical systems. They have not. Their definitions, licensing structures and treatment of particular products differ.
But both illustrate the broader point: regulation is increasingly being built around functions and risks, not simply around the name attached to a token.
That approach produces a more useful regulatory matrix.
Custody. Who controls the assets or private keys? Are client positions properly recorded and segregated? What happens if the provider fails? Which systems protect access to customer assets?
Trading. How are orders matched or executed? Is the company acting as a venue, an intermediary or a counterparty? What conflicts exist? What market-surveillance, execution and disclosure obligations apply?
Lending and yield. Where does the return come from? Can the firm reuse customer assets? Who carries counterparty and liquidity risk? What happens to withdrawals or collateral when markets are stressed?
Staking. Who controls the assets during validation? What happens if a validator is penalized? How are rewards calculated and disclosed? Can the customer exit, and under what conditions?
Issuance and distribution. Who is offering the asset? What rights does it give the holder? What disclosures are required? Does the structure itself trigger securities, stablecoin or other issuance rules?
The last category shows why token classification is not disappearing.
The legal nature of an asset still matters, particularly at issuance. A security token, stablecoin and unbacked cryptoasset may face very different requirements before anyone begins offering services around them.
But classification increasingly looks like the first layer of the regulatory analysis rather than the entire analysis.
Once an intermediary takes custody, operates a venue, lends assets or provides staking services, regulators can ask a second set of questions about what that activity does and what risks it creates.
That is a more durable basis for digital asset regulation because economic functions survive changes in product vocabulary.
A platform cannot necessarily avoid custody obligations simply by describing a customer balance as a Web3 feature if, operationally, the provider controls access to the assets. A yield product does not stop creating liquidity or counterparty risk because the return is denominated in tokens. And a matching engine does not cease to raise trading-venue questions because orders settle on a blockchain.
This approach can also reduce regulatory inconsistencies between businesses performing economically similar functions.
Crypto created unusual situations because technical architecture and legal categories did not always line up neatly. Two services could expose customers to comparable custody or execution risks while falling into very different regulatory frameworks because one was built around conventional financial instruments and the other around cryptoassets.
Activity-based rules do not eliminate those differences, but they can make the comparison more disciplined: what function is being performed, and what risk follows from it?
There is a cost.
Crypto companies often combine exchange, custody, staking, lending and payments inside a single interface. That integration is natural from a software perspective. A customer can move from holding an asset to trading it, staking it or borrowing against it without leaving the application.
Regulation sees those transitions differently.
If each function carries distinct obligations, vertically integrated platforms may need permissions covering several activities and systems capable of separating the risks attached to each one. In some cases, regulators may also impose governance or conflict-management requirements when multiple functions coexist inside the same corporate group.
That can make compliance more complicated.
But complexity alone is not evidence of bad regulation.
Traditional finance developed functional separation because combining custody, proprietary risk-taking, credit and trading can create conflicts that become especially important when a firm fails. Blockchain technology can change settlement and recordkeeping, but it does not automatically remove those economic conflicts.
Cross-border firms face an additional problem.
The activity-based logic may be spreading, but the activities themselves are not defined identically everywhere. The EU can treat a service through MiCA's crypto-asset service categories. The UK can place a similar business within its own set of regulated cryptoasset activities. Another jurisdiction may regulate the same product through payments, securities or virtual-asset rules.
A company operating globally can therefore face a paradox: regulation becomes more functional inside individual jurisdictions while the international map remains fragmented.
That is why the shift should not be described as a clean global transition from token classification to activity-based licensing.
It is better understood as an additional regulatory layer.
Classification asks what the asset is.
Activity-based regulation asks what the intermediary does with it.
Conduct rules ask how that service must treat customers.
Prudential rules ask what financial resources the provider needs to survive when things go wrong.
Those questions can coexist.
In fact, mature digital-asset regulation is increasingly likely to require all of them.
The useful regulatory question is therefore expanding from “What is this token?” toward a larger set of questions:
What service is being offered? Who controls the asset? Where does the risk sit? Who can lose money? And who is responsible when the service fails?
Token classification will remain part of the answer.
It just will not be the whole answer anymore.
Disclaimer:
This content was provided as a press release to Quantify Crypto